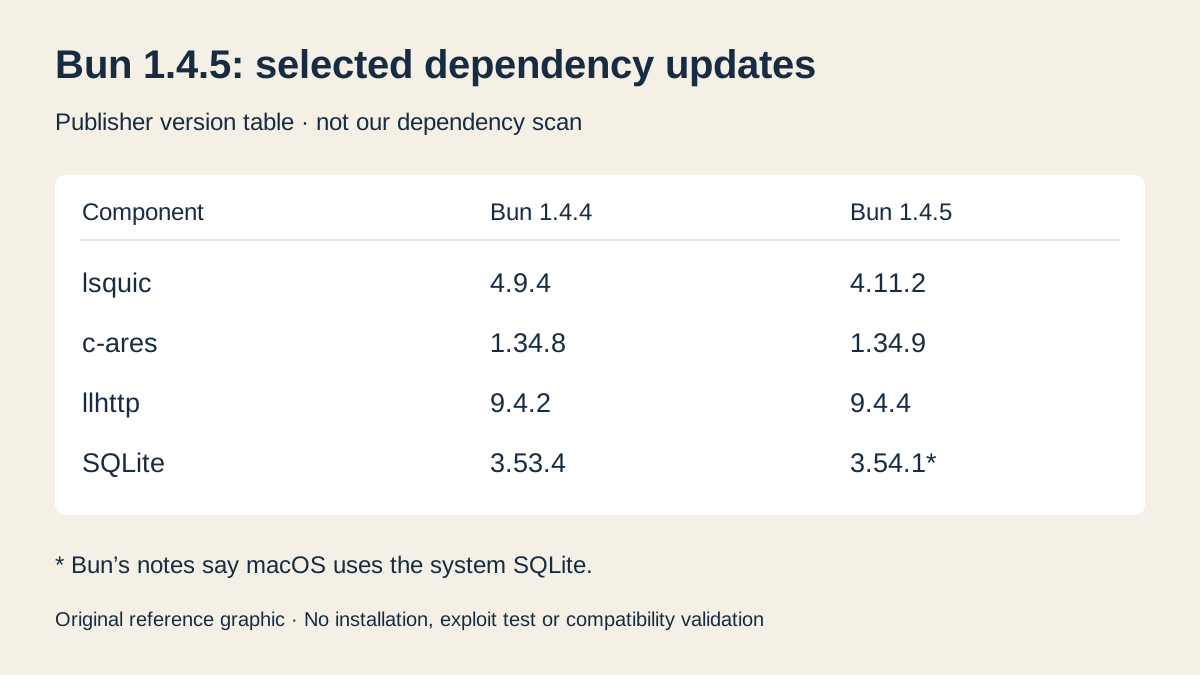

Bun’s November 19 release of 1.4.5 is designated a security update. Its announcement lists refreshed lsquic, c-ares, SQLite, llhttp and BoringSSL components, alongside networking and cryptographic compatibility fixes.
The notes identify affected surfaces across HTTP, TLS, DNS and decompression. They should be read as the publisher’s release scope, not as a finding that every application using Bun has been compromised or that we tested an exploit.
A platform distinction changes the dependency story
The announcement lists SQLite 3.54.1 but explicitly says Bun uses the system SQLite on macOS. A reader should not infer that the same runtime update replaces every platform’s SQLite with the listed bundled version.
This is a useful reminder that an application’s dependency inventory can depend on the operating system as well as the runtime package. A single version table is not a complete description of every machine on which that runtime runs.
Our analysis: identify the changed component before judging the impact
A runtime can expose one familiar API while relying on several lower-level libraries. Updating one of those components can change behavior even when application code has not changed. The right review asks which component is in use and which path reaches it.
That is more informative than treating all security releases as interchangeable. The operational impact of an updated protocol implementation can differ from a database change or a certificate-validation change. An application may depend heavily on one and barely use another.
Stricter validation can expose old assumptions
Bun also reports stricter validation of custom root certificates, with some legacy roots rejected. Its notes distinguish this from the bundled root set. We have not checked a certificate store or tested an application’s connection behavior.
A useful compatibility exercise would inspect the application’s actual trust configuration and failure handling. It should distinguish an intentional rejection from a transient network error, rather than automatically retrying until a different outcome appears.
Source licensing and linked components are separate
The tagged license document says Bun itself is MIT-licensed and describes additional terms for linked components, including JavaScriptCore. Calling every part of the distribution simply MIT would omit that boundary.
Our Bun repository profile records the qualification. We reviewed the release and license materials without installing Bun, changing this site’s toolchain, connecting to a service or independently verifying the security fixes.
EXPLORE THE SOURCE
Projects in this story
GitHub repositories
- oven-sh/bun ↗View project details
Primary-source reporting and original editorial analysis. No installation, model inference, paid service call, security test or independent benchmark performed.