MCP Inspector has published fixes for an event-stream memory problem that a connected malicious MCP server could use to crash its backend. The November 18 advisory identifies Inspector 2.16.0 and legacy 1.0.6 as patched releases.
The advisory lists affected Inspector versions 2.7.0 through 2.15.0 and versions through 1.0.5. It separately lists the legacy inspector-server package through 1.0.5. The rating is moderate; this is an availability issue, not a published claim that the flaw grants code execution.
A long-lived stream follows a different path
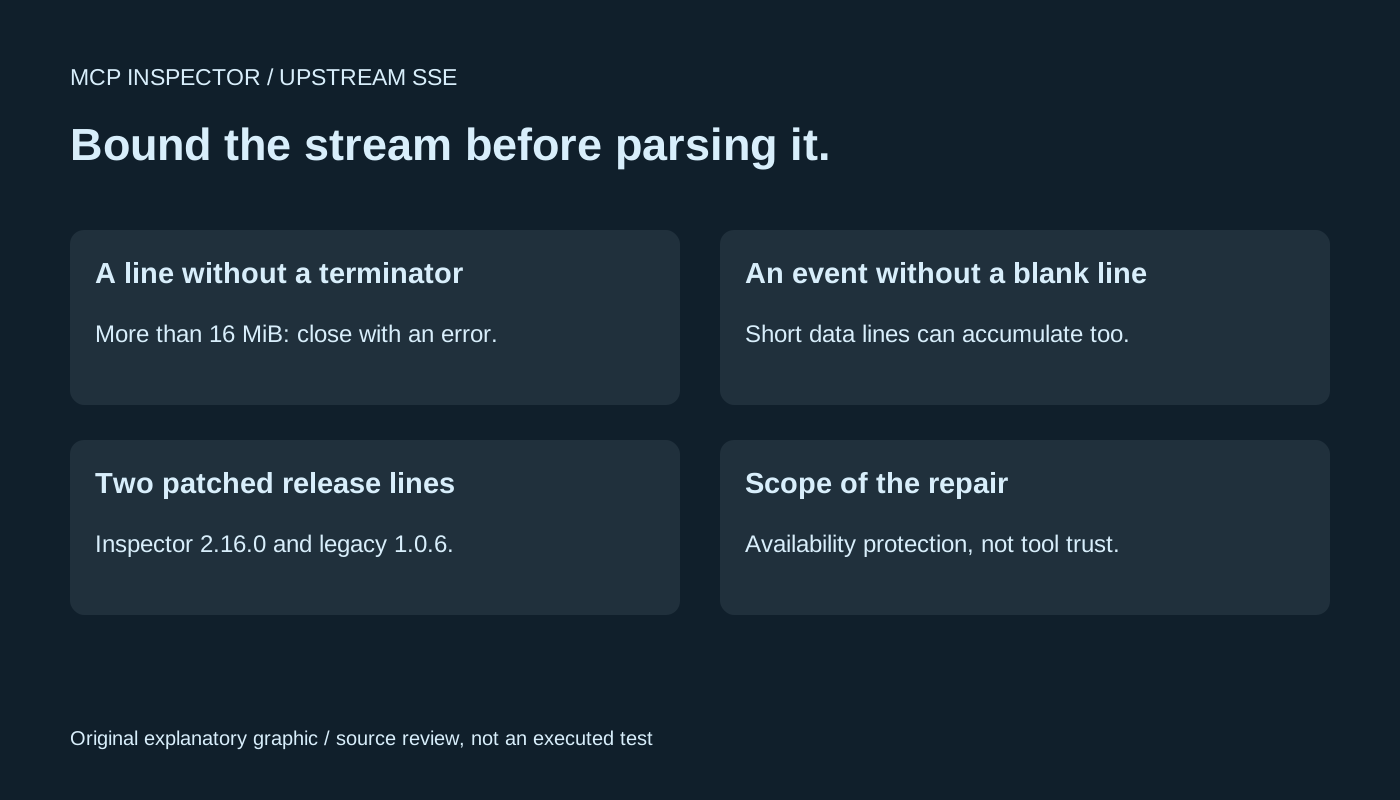
The report explains that an earlier cap on a non-long-lived response did not cover the separate GET event-stream reader. Data without an appropriate terminator could accumulate in memory while the connection stayed open.
This matters because streaming is meant to continue. A connection remaining open is not evidence that each line or event is reasonably sized. A limit on an ordinary response does not automatically apply to every streaming path.
The legacy patch bounds lines and events
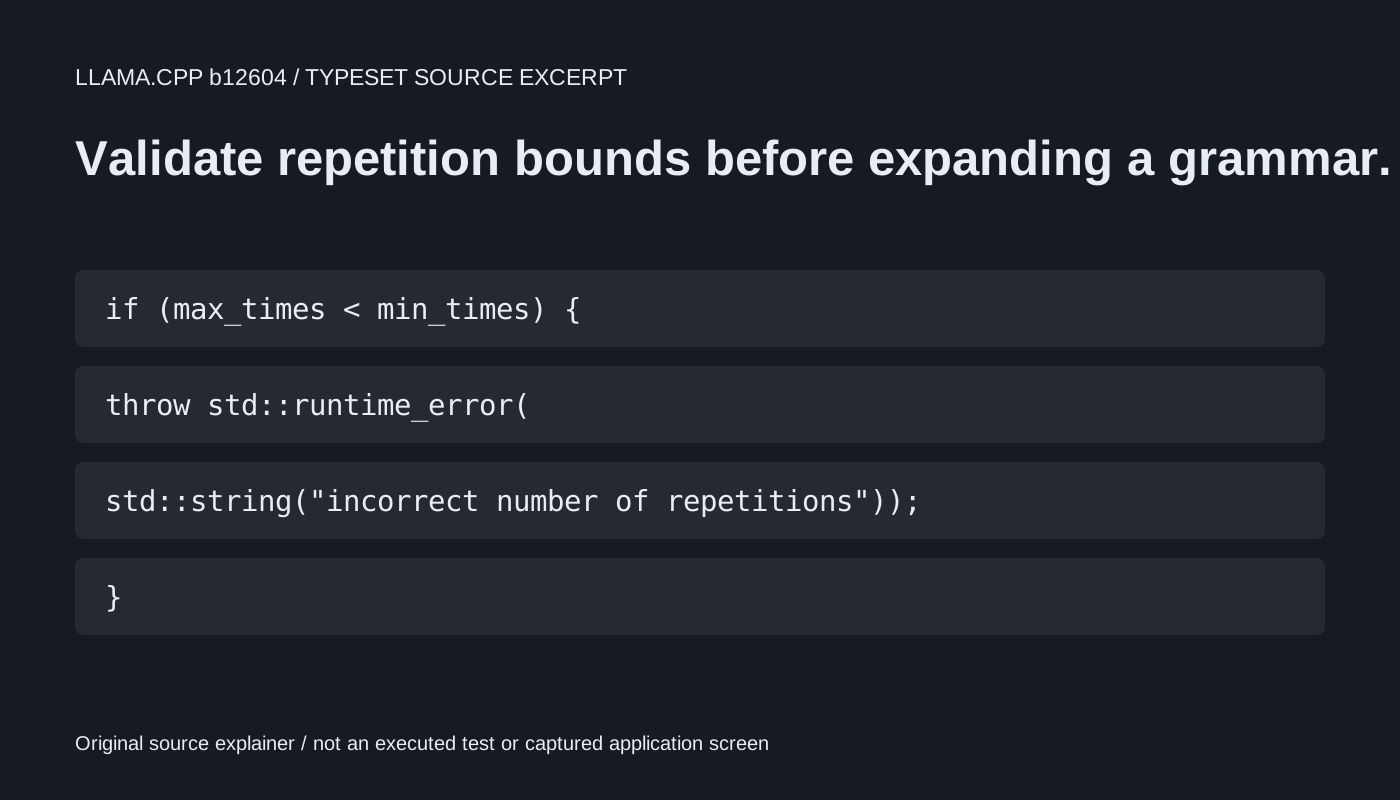
The 1.0.6 release describes a 16 MiB boundary. The tagged source checks both an unterminated line and an event assembled from short data lines without a blank line ending it.
The documented transport coverage includes SSE, Streamable HTTP and a standalone GET stream with a misleading content type. The intended failure is an error on that upstream connection instead of unbounded buffering taking down the backend. We reviewed the patch and its test code, without launching Inspector or sending an oversized stream.
Our analysis: availability controls belong at parsing boundaries
A stream can look active while making no useful progress toward a complete message. Byte limits therefore complement timeouts; neither should be assumed to replace the other. Reviewing only one response path can leave a second parser with different buffering behavior.
The repair also does not make an upstream tool trustworthy. It constrains one resource-consumption path. Authentication, tool permissions and the meaning of returned content remain separate concerns.
Our source profile records the project's licensing transition: Apache-2.0 for new or consented contributions, with unconsented earlier contributions retaining MIT terms. The v1 line is deprecated; the release also prevents its container publication from moving the v2 latest tag.
EXPLORE THE SOURCE
Projects in this story
GitHub repositories
- modelcontextprotocol/inspector ↗View project details
Original primary-source reporting and labelled editorial analysis. No installation, model download, inference, exploit attempt, upstream test suite or independent benchmark performed.